Every pull request gets a review. Before a human reads it.
Code Reviewer posts inline findings with severity, a summary, and a score on every PR. Your rules, your model, your budget.
curl -fsSL https://github.com/getkimchi/kimchi/releases/latest/download/install.sh | bash
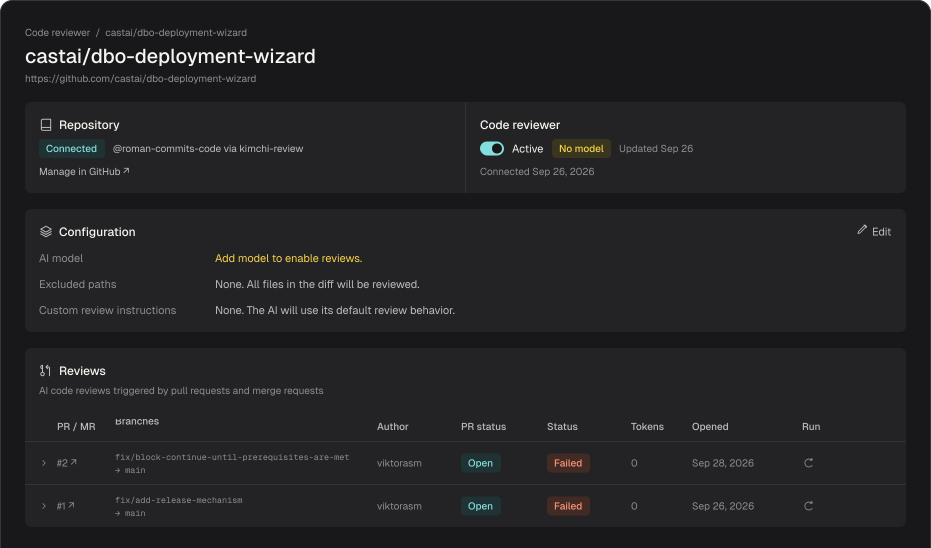




Open a PR. Get a review.
No workflow file to commit, no bot to babysit.
PR opened
A webhook fires the moment a PR opens or gets pushed to.
Diff goes to the model
Your instructions and excluded paths applied, routed to the model you picked.
Findings land inline
Findings post inline, each with a severity: critical, warning, or info.
Summary and score
One summary: score, security concerns, missing coverage.
Eight priorities, in order.
Correctness before style. Bugs before nitpicks. Same order, every review.
What lands on your pull request.
A welcome comment tracks the run. One summary closes it out.
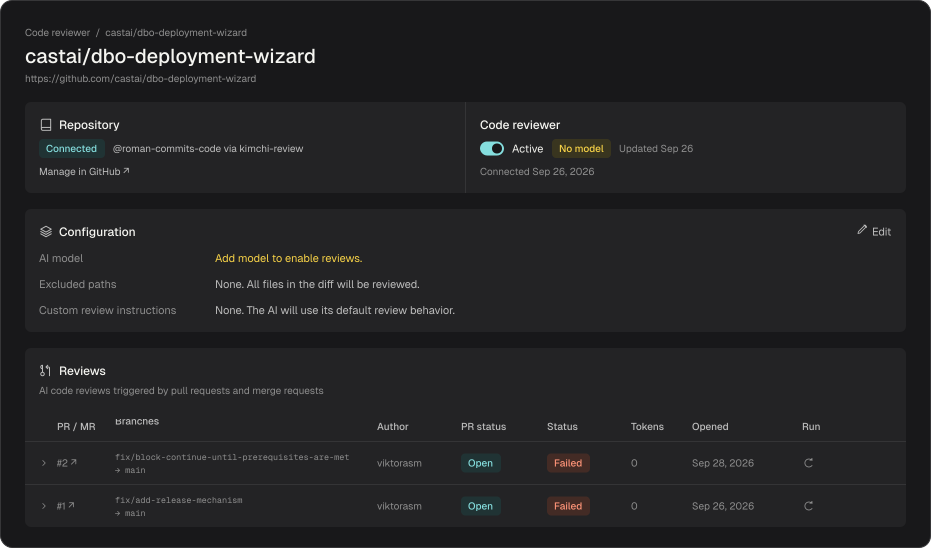
Your rules, not the bot's defaults.
Free-form instructions per repository. Exclude generated code. Pick the model. Change any of it when your standards change.
Review instructions
"Reject any PR that adds a dependency without a named owner." Your words, in every review.
Excluded paths
vendor/, generated/, dist/ - never sent to the model.
Model per repo
Most review bots hide which model reads your code. Kimchi puts it in your config.
# Review instructions, in plain language
instructions: "Reject any PR that adds a
  dependency without a named owner."

# Paths the reviewer never sees
exclude:
  - vendor/**
  - generated/**
  - dist/**

# The model that reviews this repo
model: kimi-k2.7
Reviews run inside the enforcement layer.
Reviews run on the same governed infrastructure as everything else on Kimchi.
Every review is metered
Tokens, duration, and cost per run, attributed to your org.
Reviews count against caps
Reviews are model calls. They run under the budget caps you set.
Your code is not training data
Prompts, diffs, and outputs are excluded by architecture. In any mode.
Every event stored
Webhook events are recorded for audit and replay.
Installed in minutes. No tokens to babysit.
Install the GitHub App from the console. Pick repositories. Reviews start on the next PR.
GitHub App
1-click install. Installation-scoped tokens rotate automatically. No PAT to manage.
Per-repo settings
Instructions, excluded paths, and model choice, all in the console.
GitLab
GitLab MR is enabled through a dedicated user access token or through a group access token via the GItLab API.